 Connexion


Microsoft said Tuesday that it led an industry-wide disruption of a subscription-based scam platform that used an AI chatbot to compromise 12,000 Microsoft accounts over a few-month span.
Named EvilTokens, the platform was introduced over a Telegram channel in February and charged an initial $1,500 fee and a recurring $500 charge each month after that. EvilTokens provided a single service for streamlining most steps required to compromise email accounts in large numbers. From there, the platform helped customers analyze inboxes, select targets that would provide the biggest potential payouts, and draft follow-up emails that provided realistic ruses for tricking company employees into transferring funds to attacker-controlled accounts.
“While EvilTokens helped cybercriminals access email accounts, at the center of the service was an AI-style chatbot that could analyze a victim’s inbox and help criminals identify trusted relationships, payment authorizations, and sensitive responsibilities, as well as other circumstances where fraud was most likely to succeed,” Microsoft said. “The platform could even recommend fraud strategies, including drafting messages that impersonated trusted contacts to help criminals trick victims into taking action.”
The International Meteor Organization, the nonprofit that coordinates and publishes amateur and professional observations of meteor phenomena, said its infrastructure has suffered a “critical blow” from a cyberattack.
“We recently suffered a cyberattack that dealt a critical blow to aging infrastructure, taking much of our site offline," a static page on its website on Wednesday said. “We expect several weeks of partial downtime as we transition to new infrastructure and services.”
In the meantime, the IMO said it’s prioritizing the reporting of fireball observations, which can be reported here. The organization is also providing some information on its Facebook page.
Hackers carried out a supply chain attack that installed malware on networks using an unusual technique: hijacking a chunk of Internet space where cloud management software used by hosting providers, data centers, and other large infrastructure companies is updated.
In a well-coordinated operation, the unknown attackers exploited weaknesses in the routing security setup of hosting provider Hetzner Online and the process for attaining valid TLS certificates. The lapses allowed the attackers to successfully perform a BGP (Border Gateway Protocol) hijacking to obtain control over IP addresses assigned to Softaculous. The company, based in the United Arab Emirates, is the maker of a platform for installing and managing Web software and is the developer of Virtualizor, a management platform for virtualized environments.
Softaculous used the IPs to issue updates and host a client and billing site. With control over the hijacked space, the attacker was now using the addresses to push malware masquerading as updates to unsuspecting users.
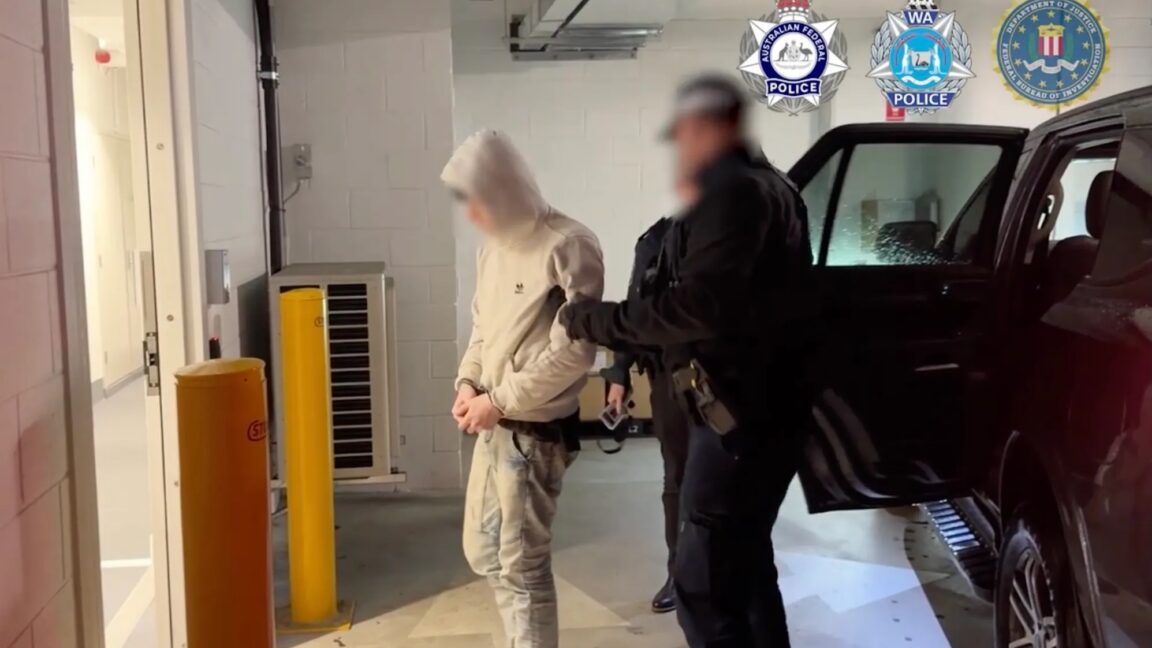
Authorities in Australia said Wednesday that they arrested two men accused of participating in cybercrimes for TeamPCP, a prolific group of hackers that, over nine months, has carried out a relentless series of supply-chain attacks that infected more than 1,000 organizations worldwide.
In a statement, the Australian Federal Police said the two men were arrested and charged with 14 offenses. The statement said the men were members of TeamPCP, which by the authorities’ count, compromised more than 1,000 organizations worldwide. The statement didn’t identify the men, except to say they lived in the Western Australian towns of Cottesloe and Mandurah. KrebsOnSecurity, citing a lengthy investigation, provided what it reports to be both defendants' names, along with an extensive background of their lives and the mistakes that led to their downfall.
TeamPCP has vexed law enforcement officials and security personnel around the world since it emerged in December. The group is best known for a sustained series of supply-chain attacks that laced open source software with malware that self-propagated from one package to another. The viral infections worked by targeting organizations’ CI/CD pipelines, which are used to rapidly develop, update, and deploy software.
Although most Americans have eschewed seasonal COVID-19 vaccines, the updated shots continue to show significant protection against cardiovascular disease, especially for those over age 75 and those with underlying medical conditions. That's according to a new study that pulled data from more than 1 million patients in a US Department of Veterans Affairs (VA) health system.
The finding builds on previous data showing that the vaccines significantly lower the risk of COVID-19-associated cardiovascular risks, particularly heart attacks and strokes. But it wasn't a given that the benefit would hold up over time—as the virus evolved, the vaccines were updated, population-level immunity increased from previous infection and vaccination, and risk of severe outcomes fell.
The new study, published in JAMA Internal Medicine, found that the 2024–2025 COVID-19 vaccine continued to protect against COVID-19-associated "major adverse cardiovascular events" (MACE), which include cardiovascular death, heart attack, stroke, and hospitalization for heart failure.
Over the decades, there has been no shortage of sites using clever techniques to covertly track visitors’ browsing histories, device fingerprints, and keystrokes and mouse movements in real time. Even Meta and Yandex were recently caught joining in the privacy-invasive free-for-all.
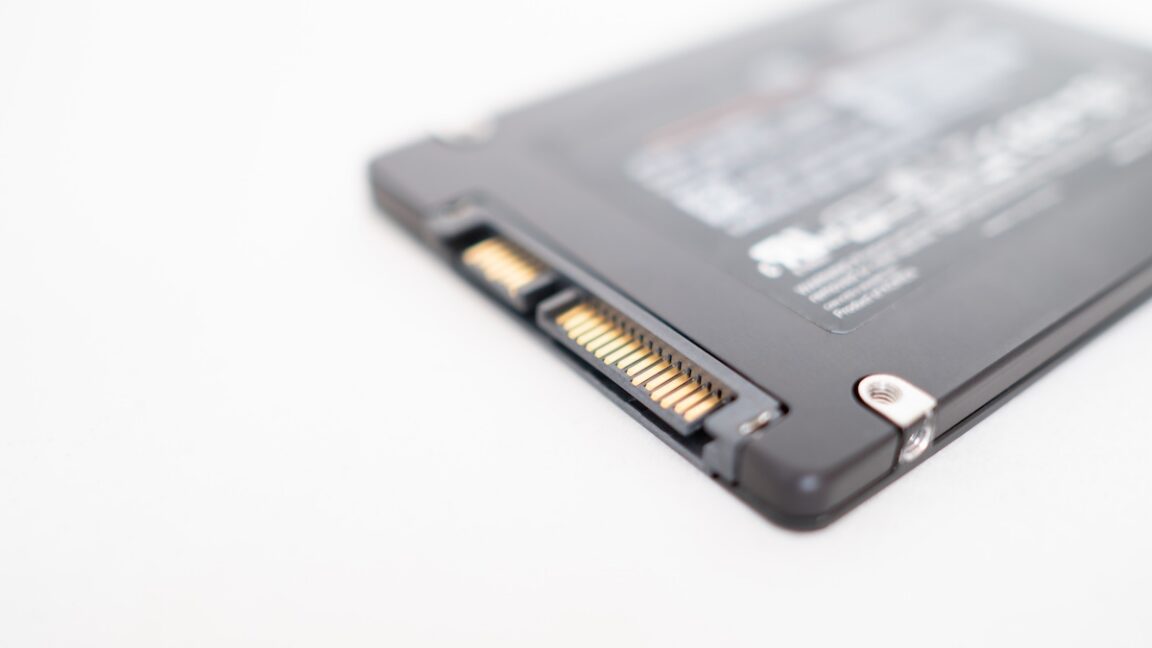
Now sites have a new way to spy on their visitors: measuring subtle interactions with their solid-state drives. The technique, named FROST (fingerprinting remotely using OPFS-based SSD timing), allows sites to monitor other sites a visitor is viewing and what apps are open on their devices.
The technique, laid out in a research paper, exploits a side channel, a form of leak resulting from physical manifestations such as electromagnetic emanations, data caches, or the time required to complete a task. By measuring the manifestations, attackers can decrypt encrypted traffic and infer other confidential data.
Chaos erupted at schools and colleges throughout the US on Thursday as a cyberattack disrupted online learning platform Canvas just as students were due to take final exams.
Canvas parent company Instructure said that as of Friday morning, the platform was back online. Instructure said it temporarily took Canvas offline on Thursday after identifying unauthorized activity in its network. The threat actor was the same one responsible for a data breach that Instructure disclosed a week ago. Data accessed included user names, email addresses, student ID numbers, and messages exchanged on the platform. The company said it has no indication that passwords, dates of birth, government identifiers, or financial information were involved.
A ransomware group known as ShinyHunters claimed responsibility for the breach on its dark web site. It claimed the data it took came from 275 million people associated with 8,800 schools.
Daemon Tools, a widely used app for mounting disk images, has been backdoored in a monthlong compromise that has pushed malicious updates from the servers of its developer, researchers said Tuesday.
Kaspersky, the security firm reporting the supply-chain attack, said it began on April 8 and remained active as of the time its post went live. Installers that are signed by the developer’s official digital certificate and downloaded from its website infect Daemon Tools executables, causing the malware to run at boot time. Kaspersky didn’t explicitly say so, but based on technical details, the infected versions appear to be only those that run on Windows. Versions 12.5.0.2421 through 12.5.0.2434 are affected. Neither Kaspersky nor developer AVB could be contacted immediately for additional details.
Infected versions contain an initial payload that collects MAC addresses, hostnames, DNS domain names, running processes, installed software, and system locales. The malware sends them to an attacker-controlled server. Thousands of machines in more than 100 countries were targeted. Out of the many machines infected, about 12 of them, belonging to retail, scientific, government, and manufacturing organizations, have received a follow-on payload—an indication that the supply-chain attack targets select groups.
Servers operated by Ubuntu and its parent company Canonical were knocked offline on Thursday morning and have remained down ever since, a situation that’s preventing the OS provider from communicating normally following the botched disclosure of a major vulnerability.
Attempts to connect to most Ubuntu and Canonical webpages and download OS updates from Ubuntu servers have consistently failed over the past 24 hours. Updates from mirror sites, however, have continued to work normally. A Canonical status page said: “Canonical’s web infrastructure is under a sustained, cross-border attack and we are working to address it.” Other than that, Ubuntu and Canonical officials have maintained radio silence since the outage began.
A group sympathetic to the Iranian government has taken credit for the outage. According to posts on Telegram and other social media, the group is responsible for a DDoS attack using Beam, an operation that claims to test the ability of servers to operate under heavy loads but, like other “stressors,” are, in fact, fronts for services miscreants pay for to take down third-party sites. In recent days, the same pro-Iran group has taken credit for DDoSes on eBay.
It has been a bad six weeks for security firm Checkmarx. Over the past 40 days, it has been the victim of at least one supply-chain attack that delivered malware to customers on two separate occasions. Now it has been hit by a ransomware attack from prolific fame-seeking hackers.
The streak of misfortunes started on March 19 with the supply-chain attack of Trivy, a widely used vulnerability scanner. The attackers behind the breach first breached the Trivy GitHub account and then used their access to push malware to Trivy users, one of which was Checkmarx. The pushed malware scoured infected machines for repository tokens, SSH keys, and other credentials.
Four days later, Checkmarx’s GitHub account was compromised and began pushing malware to the security firm’s users. The company contained and remediated the breach and replaced the malware with the legitimate apps. Or so Checkmarx thought.


 Lateo.net - Flux RSS en pagaille (pour en ajouter : @ moi)